
 AI
Information security
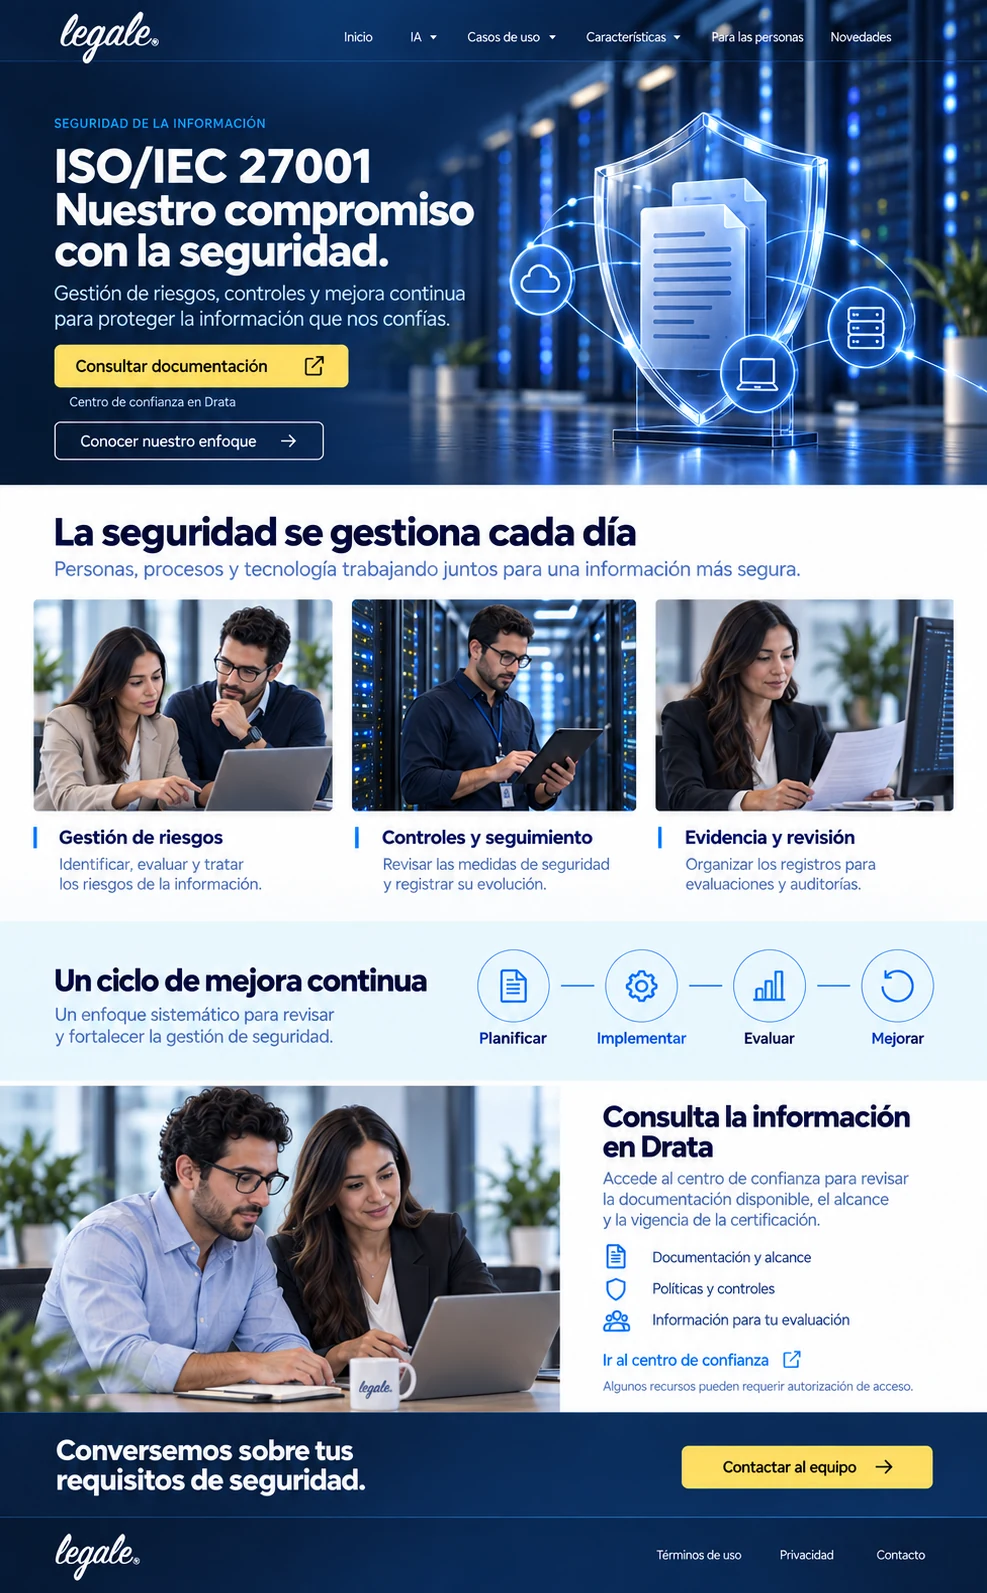
ISO/IEC 27001
Our commitment to security.
Risk management, controls and continuous improvement to protect the information you entrust to us.
Security is managed every day.
People, processes and technology working together to keep information secure.
Risk management
Identify, assess and address information security risks.
Controls and monitoring
Review security measures and track their progress.
Evidence and review
Organize records for assessments and audits.
A cycle of continuous improvement.
A systematic approach to reviewing and strengthening security management.
- Plan
- Implement
- Evaluate
- Improve
Explore information in Legale GRC
Access the Trust Center to review available documentation, certification scope and validity.
- Documentation and scope
- Policies and controls
- Information for your assessment
Some resources may require access authorization.