System and Organization Controls (SOC) 2 Type 2
SOC 2 Type 2 overview
SOC 2 TYPE 2 · CLOUD ASSURANCE
Understand the controls.
Make informed decisions.
Explore how SOC 2 reports help assess cloud service controls, understand audit coverage and support your organization’s risk review.
This guide brings together the key concepts and Microsoft cloud reporting resources referenced on this page.
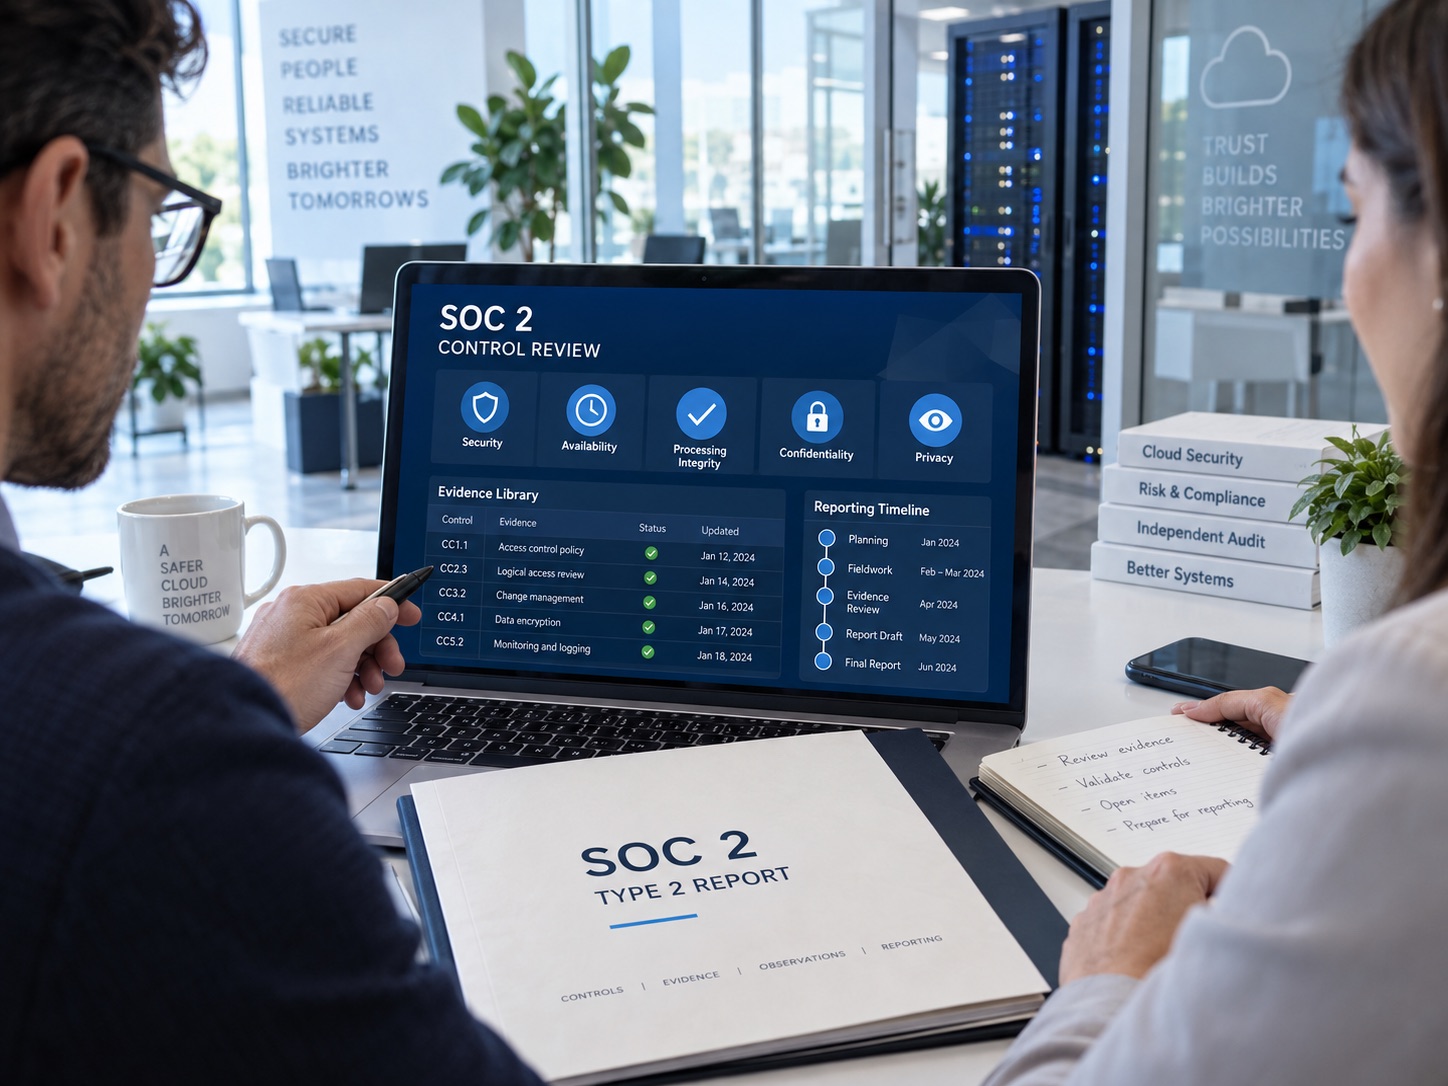
Independent examination
Read the auditor’s opinion alongside the description of the service and its controls.
Defined reporting period
Check the dates covered by the report and the evidence available for your review.
Clear responsibilities
Identify the controls your own organization needs to implement and maintain.
THE TRUST SERVICES CRITERIA
Five perspectives on trust.
SOC 2 uses the AICPA Trust Services Criteria. Review the individual report to confirm which categories and services are covered.
Security
Protection against unauthorized access.
Availability
Systems available for their intended use.
Processing integrity
Complete, accurate and authorized processing.
Confidentiality
Protection of information designated confidential.
Privacy
Handling of personal information.
UNDERSTAND THE REPORT
From control design
to operating effectiveness.
SOC 2 Type 2 examines controls over a specified period. It helps customers assess the risks associated with an outsourced service.
Read the system description, auditor’s opinion, test results and any exceptions together. The report’s scope and dates matter as much as its title.
Type 1
Addresses control design at a specified point in time.
Type 2
Also addresses how controls operated during the period under examination.
MICROSOFT CLOUD RESOURCES
Start with the services you use.
Azure & Dynamics 365
Consult the applicable Microsoft report for the service scope and examination period.
Microsoft 365
Confirm coverage for your subscription and environment, including Commercial or applicable government services.
Your organization
Map the report to your own risks, configurations and user entity responsibilities.
Microsoft reports describe Microsoft services. They do not, by themselves, establish SOC 2 attestation for Legale or for a customer’s organization.
A PRACTICAL REVIEW
Turn documentation into a clear assessment.
Confirm scope
Match the legal entity, services, environment and reporting period to the assessment you are performing.
Review the evidence
Read the findings and management responses. Keep relevant reports and supporting documents together.
Assign follow-up
Record your responsibilities, identify outstanding questions and plan the next review.
COMMON QUESTIONS
Know what you are reviewing.
Where can I find Microsoft audit reports?
Use Microsoft’s Service Trust Portal. Access requirements apply to restricted reports. The Microsoft SOC 2 documentation links to the relevant resources.
Does a bridge letter replace an audit report?
No. It provides a management statement about a period after the latest examination; it is not a new independent auditor’s report.
Where should I check service coverage?
Consult the current report and Microsoft’s official service scope documentation. Coverage can vary by service and environment.
What remains my organization’s responsibility?
Review the user entity responsibilities in the report and assess the controls relevant to your own operations and compliance requirements.
CONTINUE YOUR REVIEW
Find the evidence.
Keep the context.
Use the official Microsoft documentation for report access and scope. Visit Legale’s Trust Center for information about Legale.
A SOC 2 Type 2 attestation is performed under:
- SSAE No. 18, Attestation Standards: Clarification and Recodification, which includes AT-C section 105, Concepts Common to All Attestation Engagements, and AT-C section 205, Examination Engagements (AICPA, Professional Standards).
- SOC 2 Reporting on an Examination of Controls at a Service Organization Relevant to Security, Availability, Processing Integrity, Confidentiality, or Privacy (AICPA Guide).
- TSP section 100, 2017 Trust Services Criteria for Security, Availability, Processing Integrity, Confidentiality, and Privacy (AICPA, 2017 Trust Services Criteria).
In addition, the Office 365 SOC 2 Type 2 attestation report addresses the requirements set forth in the Cloud Security Alliance (CSA) Cloud Controls Matrix (CCM), and the Cloud Computing Compliance Criteria Catalog (C5:2020) created by the German Federal Office for Information Security (BSI).
Office 365 SOC 2 attestations are based on rigorous comprehensive third-party examinations (also known as audits) conducted by an independent AICPA accredited CPA firm. At the conclusion of a SOC 2 audit, the auditor renders an opinion in a SOC 2 Type 2 report, which describes the cloud service provider’s (CSP) system and assesses the fairness of the CSP’s description of its controls. It also evaluates whether the CSP’s controls are designed appropriately, were in operation on a specified date, and were operating effectively over a specified time period. Office 365 SOC 2 Type 2 reports are relevant to system Security, Availability, Processing Integrity, Confidentiality, and Privacy.
Microsoft in-scope cloud platforms & services
Microsoft online services in scope are shown in the Azure SOC 2 Type 2 attestation report:
- Azure (for detailed insight, see Microsoft Azure Compliance Offerings)
- Azure DevOps (see separate Azure DevOps SOC 2 Type 2 attestation report)
- Dynamics 365 (for detailed insight, see Azure SOC 2 Type 2 attestation report)
- Microsoft Defender XDR
- Microsoft Defender for Cloud Apps
- Microsoft Defender for Endpoint
- Microsoft Defender for Identity
- Microsoft Forms Pro
- Microsoft Intune
- Microsoft Managed Desktop
- Microsoft Stream
- Microsoft Threat Experts
- Topics
- Nomination Portal
- Office 365, Office 365 U.S. Government, Office 365 U.S. Government – High, Office 365 U.S. Government Defense
- Power AppsPower Automate
- Power BI
- Power Virtual Agents
- Update Compliance
Azure, Dynamics 365, and SOC 2
For more information about Azure, Dynamics 365, and other online services compliance, see the Azure SOC 2 offering.
Office 365 and SOC 2
Office 365 environments
Microsoft Office 365 is a multi-tenant hyperscale cloud platform and an integrated experience of apps and services available to customers in several regions worldwide. Most Office 365 services enable customers to specify the region where their customer data is located. Microsoft may replicate customer data to other regions within the same geographic area (for example, the United States) for data resiliency, but Microsoft will not replicate customer data outside the chosen geographic area.
This section covers the following Office 365 environments:
- Client software (Client): commercial client software running on customer devices.
- Office 365 (Commercial): the commercial public Office 365 cloud service available globally.
- Office 365 Government Community Cloud (GCC): the Office 365 GCC cloud service is available for United States Federal, State, Local, and Tribal governments, and contractors holding or processing data on behalf of the US Government.
- Office 365 Government Community Cloud – High (GCC High): the Office 365 GCC High cloud service is designed according to Department of Defense (DoD) Security Requirements Guidelines Level 4 controls and supports strictly regulated federal and defense information. This environment is used by federal agencies, the Defense Industrial Base (DIBs), and government contractors.
- Office 365 DoD (DoD): the Office 365 DoD cloud service is designed according to DoD Security Requirements Guidelines Level 5 controls and supports strict federal and defense regulations. This environment is for the exclusive use by the US Department of Defense.
Use this section to help meet your compliance obligations across regulated industries and global markets. To find out which services are available in which regions, see the International availability information and the Where your Microsoft 365 customer data is stored article. For more information about Office 365 Government cloud environment, see the Office 365 Government Cloud article.
Your organization is wholly responsible for ensuring compliance with all applicable laws and regulations. Information provided in this section does not constitute legal advice and you should consult legal advisors for any questions regarding regulatory compliance for your organization.
Office 365 applicability and in-scope services
Use the following table to determine applicability for your Office 365 services and subscription:
Applicability
In-scope services
Commercial
Compliance Manager, Customer Lockbox, Delve, Exchange Online Protection, Exchange Online, Forms, Griffin, Identity Manager, Lockbox (Torus), Microsoft Teams, Microsoft Viva Topics, MyAnalytics, Office 365 Customer Portal, Office 365 Microservices (including but not limited to Kaizala, ObjectStore, Sway, PowerPoint Online Document Service, Query Annotation Service, School Data Sync, Siphon, Speech, StaffHub, eXtensible Application Program), Office Online, Office Services Infrastructure, OneDrive for Business, Planner, PowerApps, Power Automate, Power BI, Project Online, Service Encryption with Microsoft Purview Customer Key, SharePoint Online, Skype for Business
GCC
Microsoft Entra ID, Compliance Manager, Delve, Exchange Online, Forms, Microsoft Defender for Office 365, Microsoft Teams, Microsoft Viva Topics, MyAnalytics, Office 365 Advanced Compliance add-on, Office 365 Security & Compliance Center, Office Online, Office Pro Plus, OneDrive for Business, Planner, PowerApps, Power Automate, Power BI, SharePoint Online, Skype for Business, Stream
GCC High
Microsoft Entra ID, Exchange Online, Forms, Microsoft Defender for Office 365, Microsoft Teams, Office 365 Advanced Compliance add-on, Office 365 Security & Compliance Center, Office Online, Office Pro Plus, OneDrive for Business, Planner, PowerApps, Power Automate, Power BI, SharePoint Online, Skype for Business
DoD
Microsoft Entra ID, Exchange Online, Forms, Microsoft Defender for Office 365, Microsoft Teams, Office 365 Advanced Compliance add-on, Office 365 Security & Compliance Center, Office Online, Office Pro Plus, OneDrive for Business, Planner, Power BI, SharePoint Online, Skype for Business
Office 365 environments
- Office 365 Core – SSAE 18 SOC 2 Report
- Office 365 Microservices T1-SSAE 18 SOC2 Type I Report
- See bridge letters and additional audit reports
In accordance with AICPA requirements, you must have an existing subscription or free trial account in Office 365 or Office 365 U.S. Government to download SOC 1 and SOC 2 attestation reports and any bridge letters as needed.
Frequently asked questions
In accordance with AICPA requirements, you must have an existing subscription or free trial account in Office 365 or Office 365 US Government to download SOC 1 and SOC 2 attestation reports and any bridge letters as needed.
Microsoft commissions a full SOC 1 Type 2 and SOC 2 Type 2 examination of Office 365 annually. The auditor’s reports on these examinations (also known as audits) are issued as soon as they’re ready after that audit. The SOC 3 report, which is based on the SOC 2 examination, is issued at the same time.
Because Microsoft doesn’t control the investigative scope of the examination nor the timeframe of the auditor’s completion, there’s no set timeframe when these reports are issued. The reports are usually issued a few months after the end of the period under examination. Microsoft doesn’t allow any gaps in the consecutive periods of examination from one examination to the next.
Microsoft also commissions a mid-year SOC 1 Type 1 and SOC 2 Type 1 examination of Office 365 for new Microsoft services that have been issued since the last SOC Type 2 audit. Type 1 audits don’t look back over a period of performance.
Due to the sophisticated nature of Office 365, the service scope is large if examined as a whole. This can lead to examination completion delays simply due to scale. Microsoft organizes all the examinations described above into 2 categories: Core Services and Microservices. Microsoft issues a report scoped to each examination.
SOC Type 2 audits examine a rolling 12-month run window (also known as audit period or more formally period of performance) with examinations conducted annually for the period 1-October through 30-September of the next calendar year. The examination starts promptly after the period of performance is complete.
Microsoft also issues bridge letters (also known as gap letters). These are self-attestations by Microsoft, not reports based on examinations by the auditor. Bridge letters are issued during the current period of performance that is not yet complete and ready for audit examination. Microsoft issues bridge letters at the end of each quarter to test our performance during the prior three-month period. Due to the period of performance for the SOC type 2 audits, the bridge letters are typically issued in December, March, June, and September of the current operating period.
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Sed do eiusmod tempor incididunt ut labore et dolore magna aliqua.
Use Microsoft Purview Compliance Manager to assess your risk
Microsoft Purview Compliance Manager is a feature in the Microsoft Purview compliance portal to help you understand your organization’s compliance posture and take actions to help reduce risks. Compliance Manager offers a premium template for building an assessment for this regulation. Find the template in the assessment templates page in Compliance Manager. Learn how to build assessments in Compliance Manager.
Resources
- Service Trust Portal audit reports
- AICPA SOC for Service Organizations
- SSAE No. 18, Attestation Standards: Clarification and Recodification (AICPA Professional Standards)
- SOC 2 Reporting on an Examination of Controls at a Service Organization Relevant to Security, Availability, Processing Integrity, Confidentiality, or Privacy (AICPA Guide)
Hear directly from our valued customers!
-
Himura Adreas CEO at ManikaAfter evaluating different alternatives, we decided to integrate Despapeliza's document management platform due to a need to move forward as a company towards digitalization. Thanks to the autonomy in configuration, we have covered different areas of the company, automating internal and external workflows, managing to eliminate paper and save resources. Our users have become accustomed to the ease of the platform, demanding digitalization in more company processes.
Read more -
Lucy Rodriguez Administration LeaderThanks to the ease of use of the solution, we achieved rapid adoption of the tool and reduced signing times from 7 days to just hours in processes of board minutes, committees and commercial agreements. We save 100% of the expenses associated with the transportation of documents and the collection of signatures in different communities, and even outside Santiago.
Read more
Legale.io Makes Headlines!


AI